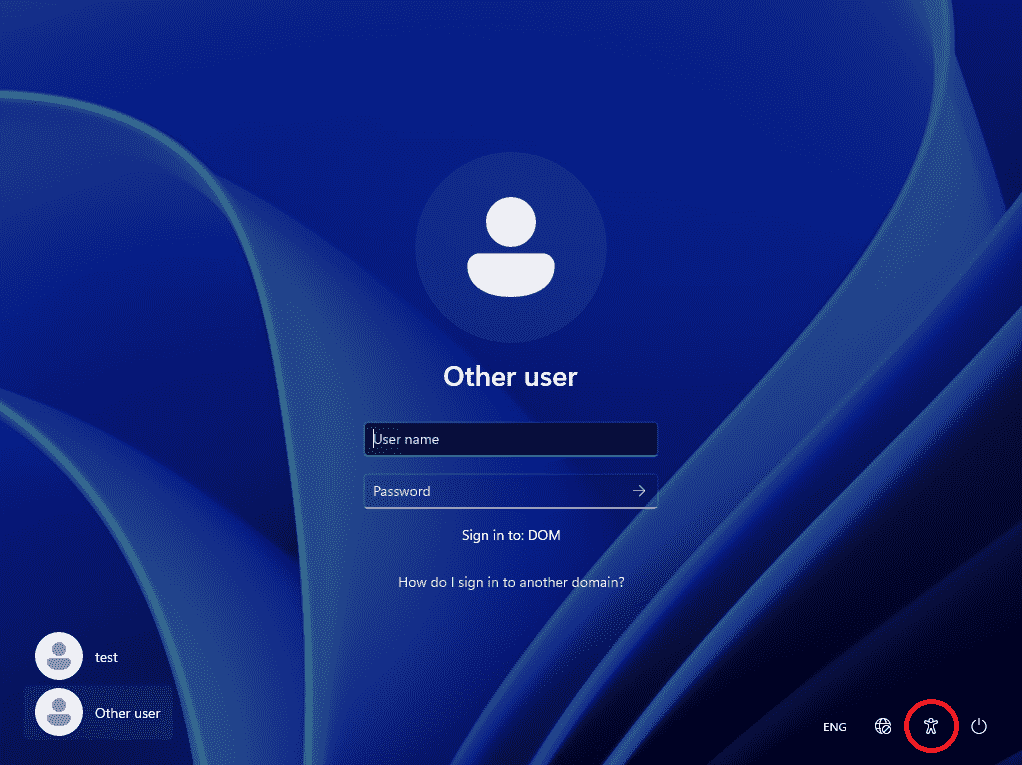
A deep dive into Windows authentication bypass through offline file manipulation — covering the classic Utilman trick, how it maps to MITRE ATT&CK T1546.008, and how defenders can detect and prevent it.
#Windows#Red Team#MITRE ATT&CK#Authentication