Offensive security write-ups & research
CVE breakdowns, red team tradecraft, tooling, and lessons from real engagements.
Inside CVE-2025-55182: Weaponising the React2Shell RCE
How a server-side rendering flaw in a popular React framework became a full remote code execution chain — and…
Havoc C2 in Practice: Lessons From 200+ Engagements
What actually matters when you're running Havoc C2 against a live target — from OPSEC to persistence to knowi…
OWASP API Top 10 in the Real World: What I Actually Find
A breakdown of which OWASP API Top 10 categories show up most often across dozens of API pentests — and which…
From Bug Bounty to Senior VAPT Engineer: What Changed
The mindset and skill shifts that mattered most moving from freelance bug hunting to leading a pentest team.
Active Directory Attack Paths I See Most Often
A field-tested rundown of the AD misconfigurations that reliably lead to domain compromise.
Building a Passive Recon Scanner Without Touching the Target
Notes from building a single-file, dependency-free CMS fingerprinting tool for early-stage recon.
More write-ups from the field
Long-form research, walkthroughs and analysis published on my Medium profile.
 Medium
Compliance-Based Penetration Testing: What Most Pentesters Get Wrong
Lessons from 250+ engagements, and the misconceptions I keep running into.
 Medium
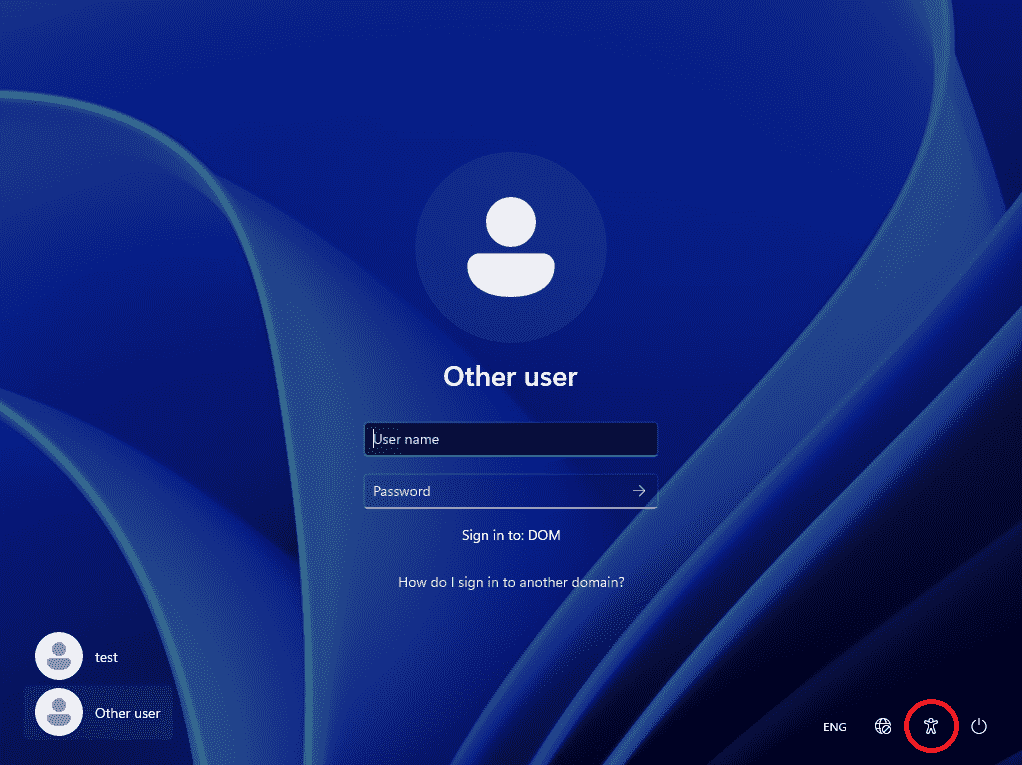
Beyond the Utilman Trick: Offensive Analysis of Windows Authentication Bypass
An offensive security analysis of Windows authentication bypass via offline file manipulation.
 Medium
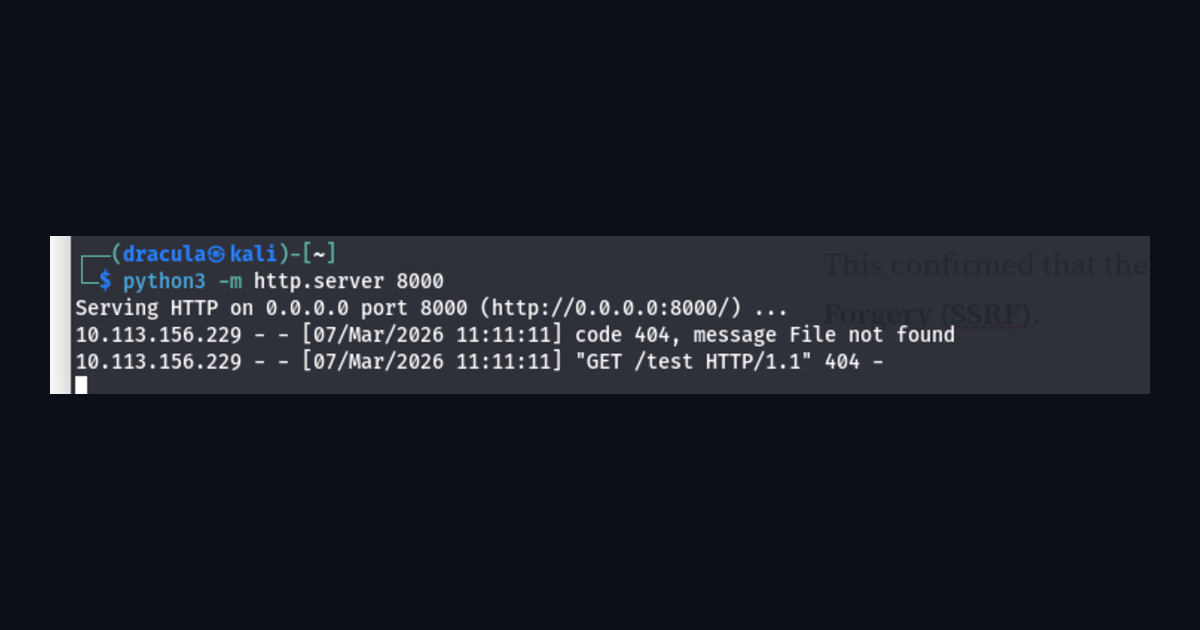
TryHackMe MD2PDF Write-up — Exploiting Markdown-to-PDF for SSRF
Exploiting a Markdown-to-PDF pipeline for server-side request forgery in the MD2PDF challenge.
Get offensive security briefings
New write-ups, CVE breakdowns and tooling — straight to your inbox.